1. Data Protection (PII)
Block agents from sharing PII outside the company.
rules:
  - id: block-pii-sharing
    when:
      output.contains("pii")
    then: deny
message: "Sharing PII is not allowed"SuperAgentX Policy Engine enforces your rules before any AI action happens — so every request is safe, compliant, and auditable by design.
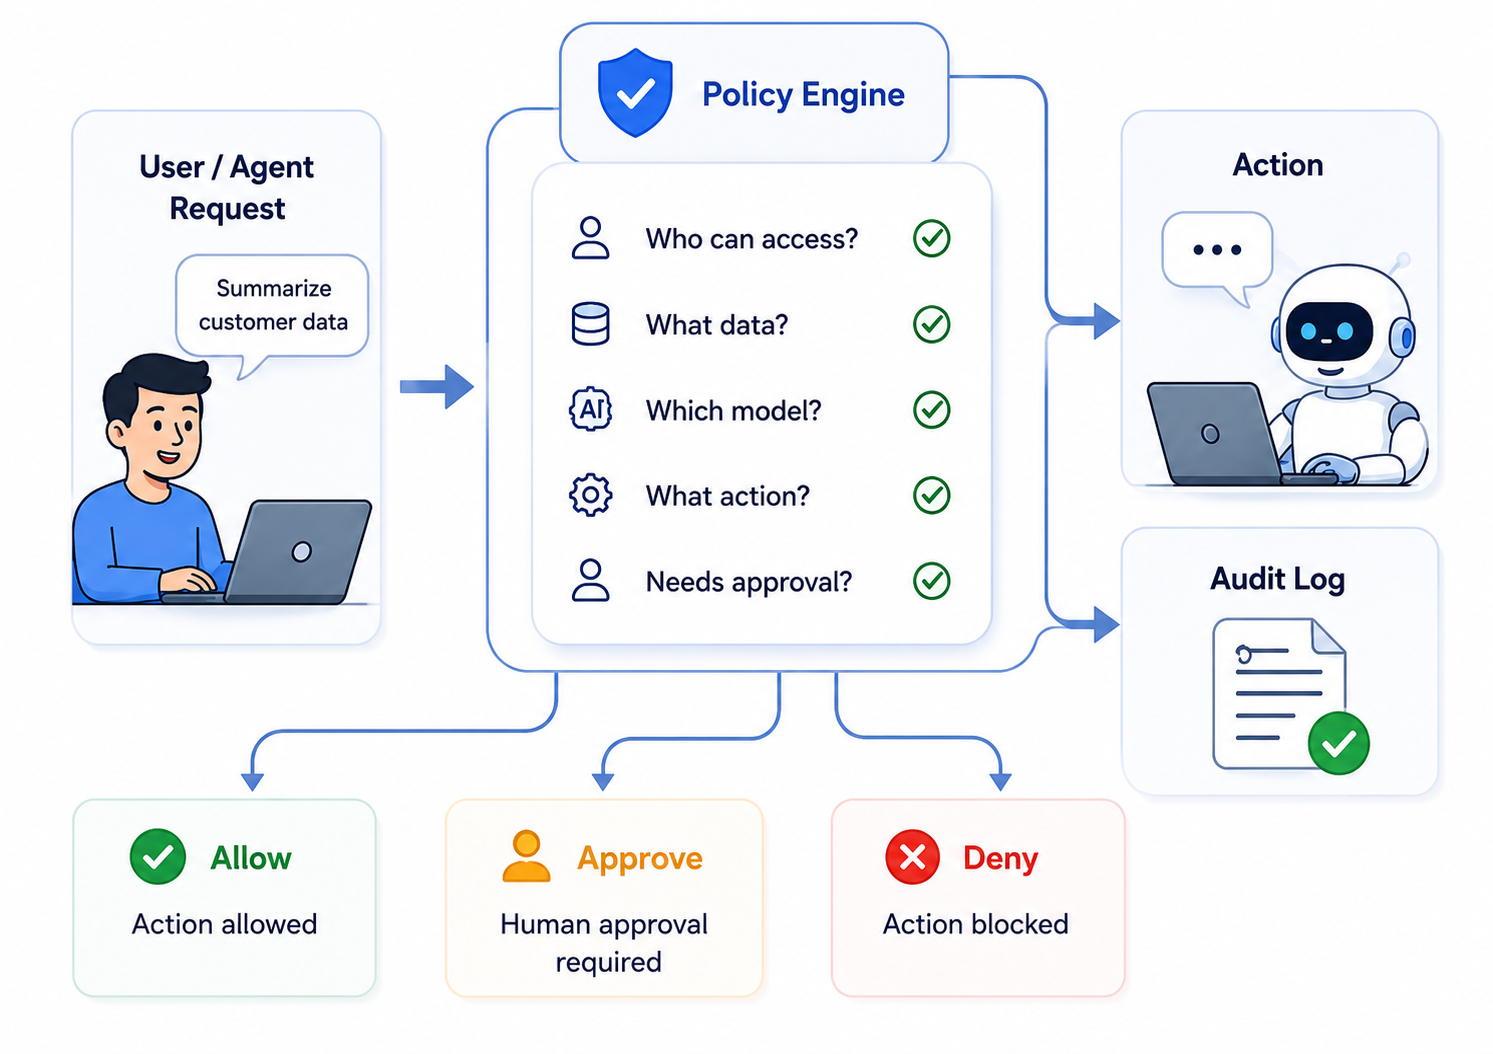
Every request is evaluated in real time against your policies before any AI action is executed.
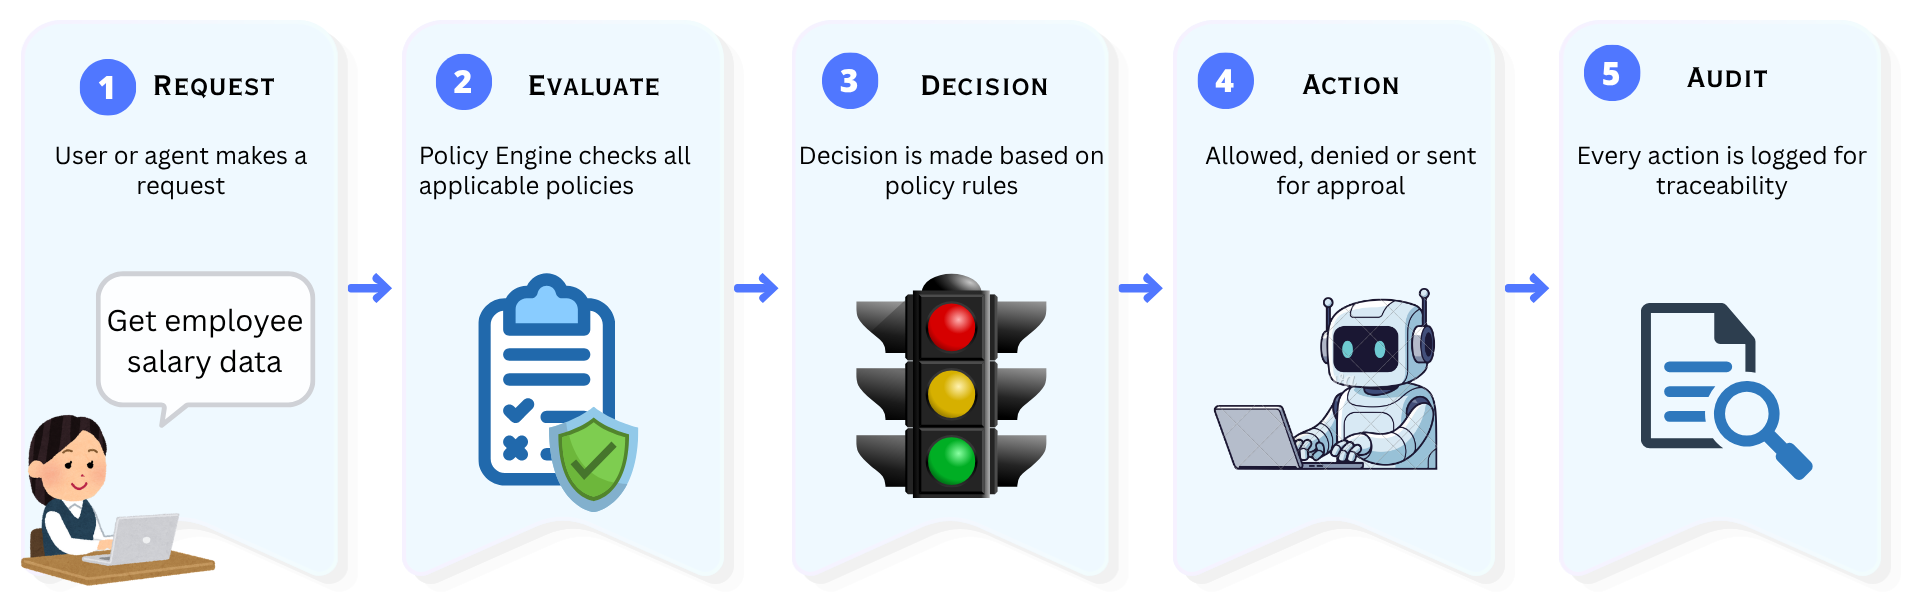
Define rules in simple YAML — enforce them across every agent, workflow, and tool.
Block agents from sharing PII outside the company.
rules:
- id: block-pii-sharing
when:
output.contains("pii")
then: deny
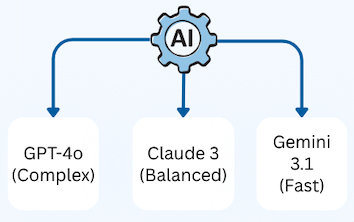
message: "Sharing PII is not allowed"Use the right model based on the task type.
rules:
  - id: route-by-task
    when: task.type == "complex"
    then: use_model: "gpt-4o"
    else_if: task.type == "fast"
then: use_model: "gemini-1.5"Restrict high risk actions in production environment.
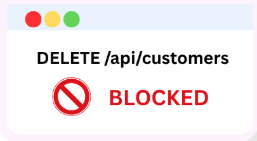
rules:
  - id: block-delete-prod
    description: Block destructive API calls in production
    scope: tool
    when:
      env: production
      action: delete
decision: denyOnly allow specific teams to use certain models.
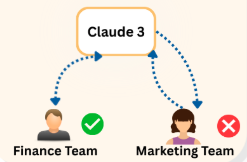
rules:
  - id: model-access
    description: Restrict model access by team
    scope: model
    when:
      team: finance
      model: claude-3
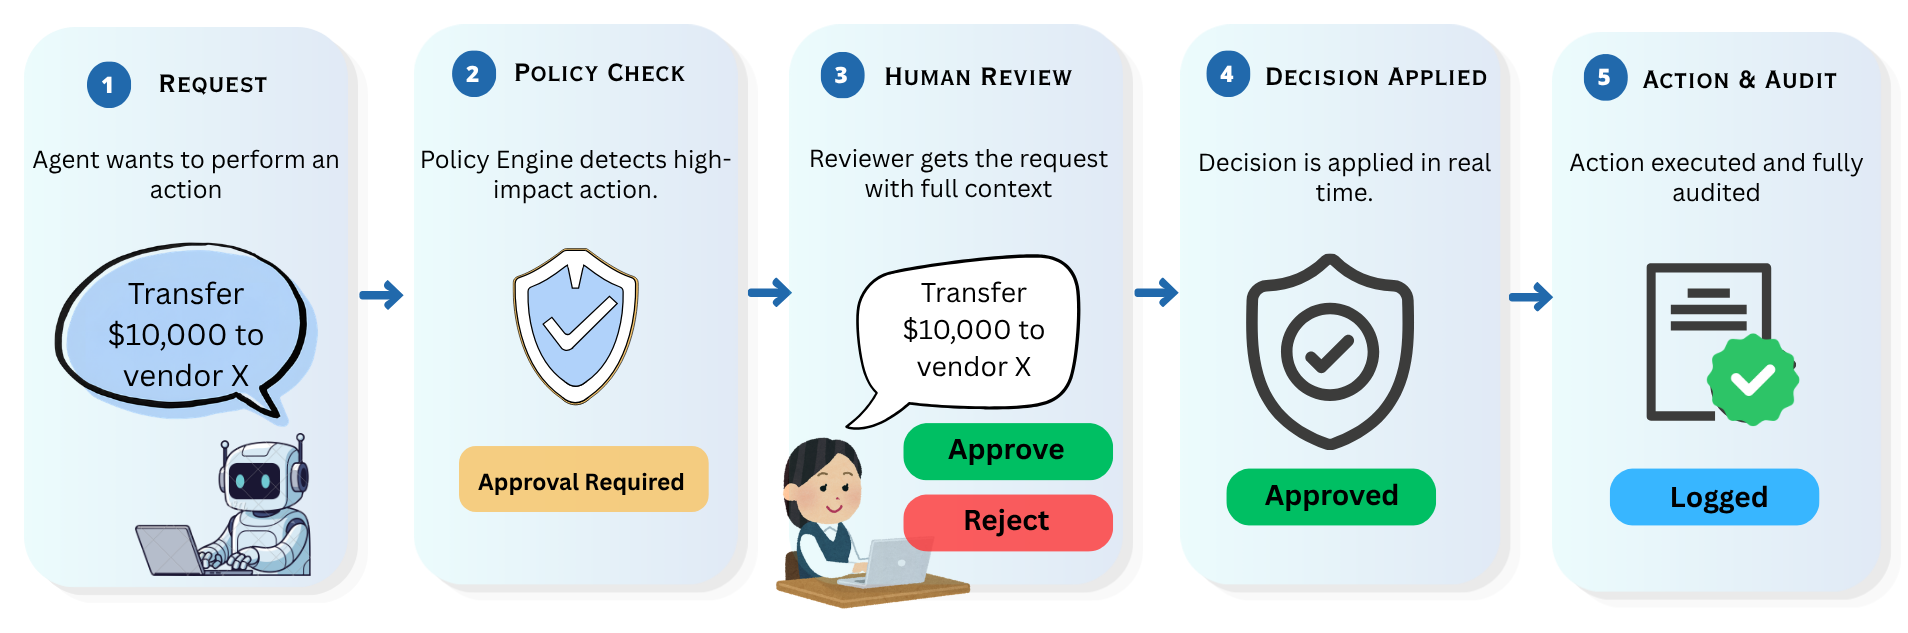
decision: allowRequire human approval for high-impact actions — with full context and audit trails.